 Sealfie
Arup: he verified, and the verification lied
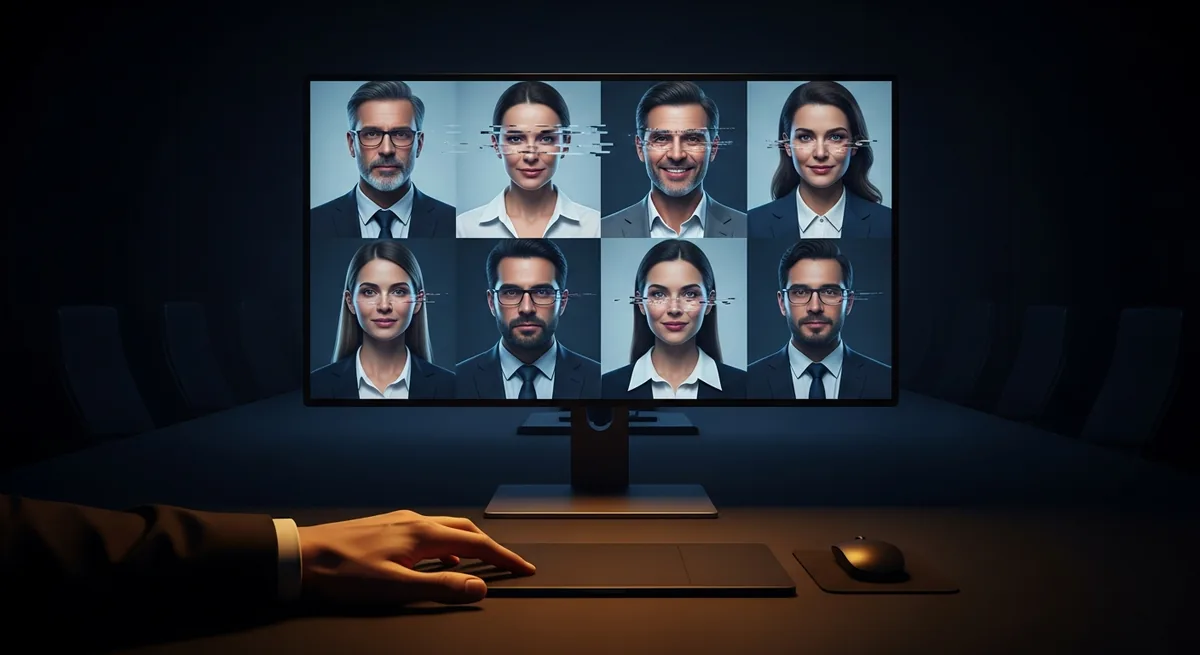
January 2024, Hong Kong. A finance employee at the British engineering group Arup receives an email presenting itself as coming from the group’s UK-based chief financial officer, asking for a confidential and urgent transaction.
He does not believe it. Unusual request, demand for secrecy, pressure on the timeline: he ticks off, one by one, the boxes his awareness programme taught him to recognise. He refuses to act on that email alone.
He is then offered a video call. The CFO appears on screen, surrounded by several colleagues. Faces he knows, voices he recognises, the right intonation. The doubt collapses. He then executes fifteen separate transfers to five bank accounts, totalling around 25 million dollars. He discovers the fraud only later, when he raises the operation with head office.
The sequence says the opposite of what people take from it
The case circulates as an illustration of human inattention. The chronology tells another story. This employee suspected fraud at first contact, he refused to execute on an email alone, and he went looking for confirmation through a second channel. Those three moves are exactly what any awareness programme exists to produce. He made all three.
Then he verified. And the verification lied to him.
The attack did not bypass his control point. It moved inside it.
Fifteen transfers, fifteen chances to reconsider
The detail that makes the case instructive is the count. Fifteen transfers to five accounts form a series spread over time, far from one impulsive click on a Friday evening. Fifteen moments, then, when vigilance could have woken up.
It did not, for a simple reason: it had already done its job and been given an answer. A control that has returned its verdict closes the question for everything that follows. That is precisely what a control is for, and it is what makes its corruption so expensive.
The verification channel became the target
For twenty years, training designated the inbound channel as the terrain of the attack: the suspicious email, the trapped link, the attachment. The outbound channel, the one you use to call back and confirm, was assumed safe because it started with us.
Real-time identity synthesis removed that asymmetry. A video call, a voice on the phone, a familiar face in a virtual meeting room: all of these are now manufactured at negligible cost, at a quality sufficient to hold thirty minutes of professional conversation. The safety net became the vector.
What awareness training can produce, and what it cannot
The Arup employee had taken the courses. He applied their content rigorously. The problem sits one level above behaviour: he was being asked to recognise in real time, under hierarchical pressure, what specialised automated systems cannot identify.
The measurement exists. In March 2025, researchers from CSIRO, Australia’s national science agency, and Sungkyunkwan University published an analysis of 51 deepfake detectors, sixteen of them tested under real-world conditions. None of the sixteen reliably identified real-world deepfakes. Training a human to outperform those sixteen tools moves the failure rate by a few points. The nature of the task being asked stays the same.
Where the law now puts the loss
The liability question is being settled, and it is not being settled on the employee. UCC Article 4A allocates the loss on a fraudulent wire to the party whose security procedures were not commercially reasonable, a test about procedures that execute rather than people who were briefed. The SEC’s 2023 cybersecurity rules point the same way by making the governance of those procedures a board-level disclosure item, which carries the question up to the people who sign the filing.
That allocation matches what happened in Hong Kong. Punishing the man who doubted and then verified would make no sense: he operated the system exactly as it had been described to him. The system returned the wrong verdict.
Three requirements for a channel that does not lie
So restate the question. What structural controls can create technical friction between a payment request and its execution, even when every face in the room looks familiar? The principle rests on three conditions.
First, no authorisation depends on a single signal. What you need is a bundle, where any one element can be forged without the whole being forged.
Second, those elements come from genuinely independent sources. None can be compromised through the same access as its neighbour, and they are operated by IT and security professionals rather than by the team executing the transfer.
Third, the bundle is shared with whoever receives the instruction, not merely held by whoever issues it. That sharing separates an irrefutable trace from a plain assertion. Under those three conditions, what the employee sees and hears stops being the deciding factor. How Sealfie works rests on that principle.
The Arup employee did everything he had been taught. The next one deserves a verification channel that holds.
Size your exposure
The BEC risk calculator estimates your company’s annual incident probability and expected loss in six questions, with a published methodology and sourced coefficients. No data leaves your browser.